
Security your airline can audit
PCI DSS v4.0.1 service-provider compliant. Hosted on Google Cloud in Frankfurt. Externally penetration-tested every year.
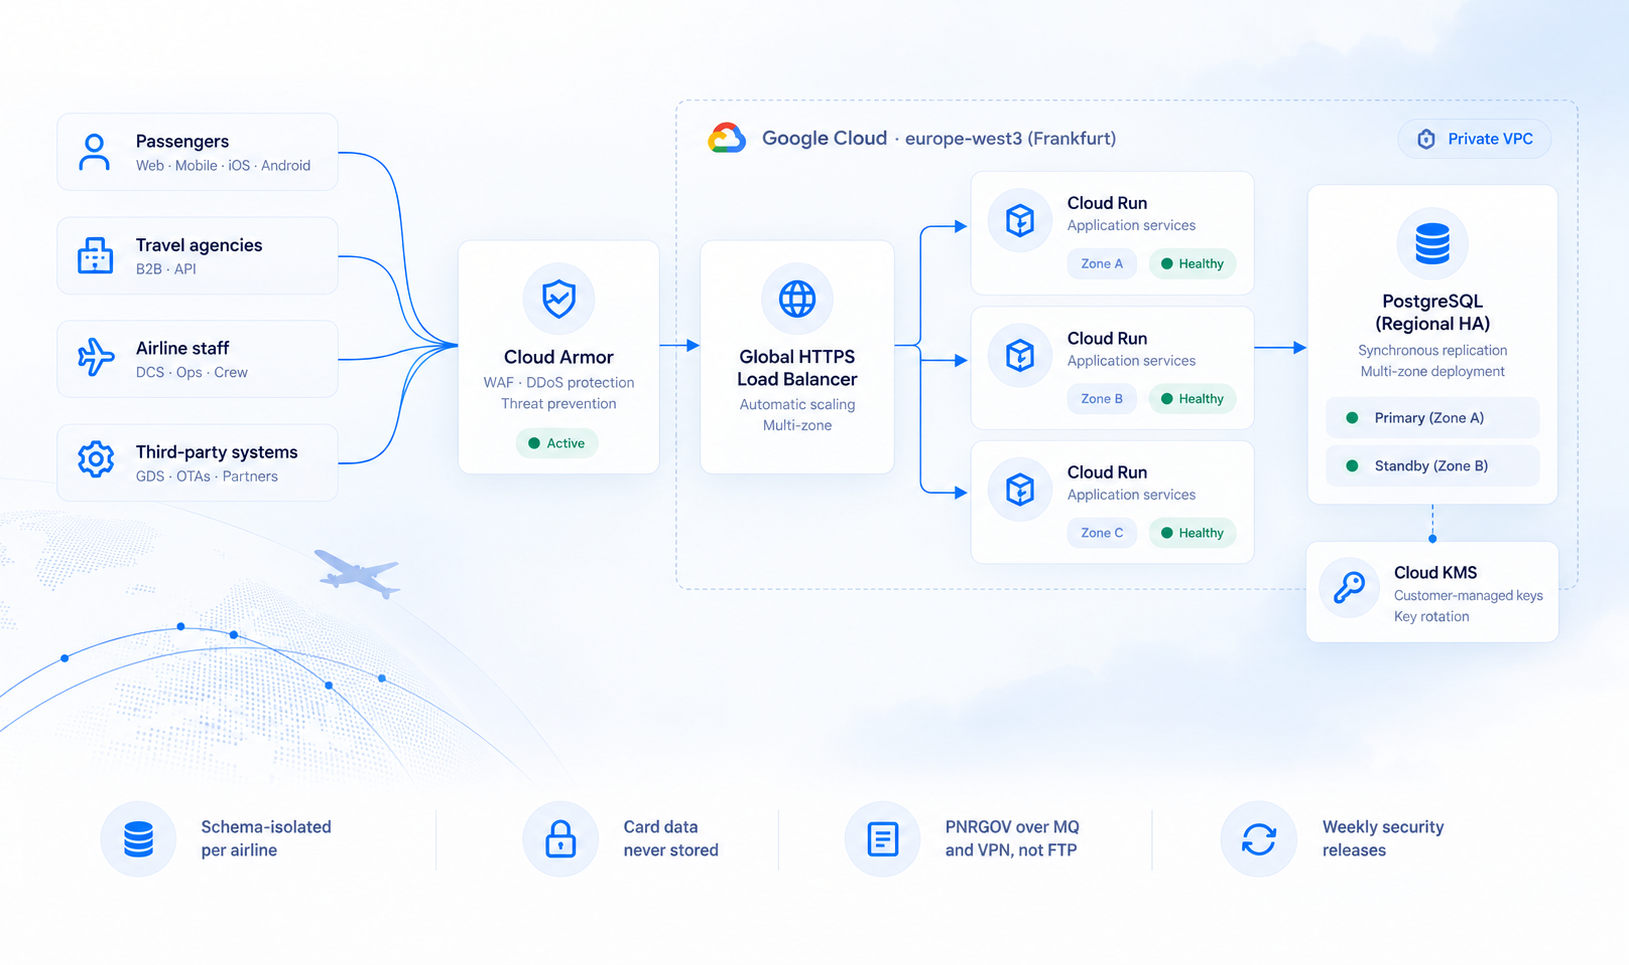
- Schema-isolated per airline
- Card data never stored
- PNRGOV over MQ and VPN, not FTP
- Weekly security releases

Where airline software security breaks
Most PSS platforms were built before cloud zones, bot traffic, and supply-chain attacks were the threat.
Batch sync, batch failure
When one vendor's overnight sync breaks, every airline on the platform wakes up with stale inventory and no check-in.
Shared credentials, shared breach
Common admin logins and long-lived API keys mean one leaked credential exposes every carrier's PNRs.
Plaintext regulatory traffic
PNRGOV, PAXLST, and APIS still move over FTP and aging SITA links at most carriers.
Bots blocking inventory
Speculative holds, OTP pumping, and scripted account creation sit on the booking funnel and nobody measures them.

Isolated by schema, scoped at the door
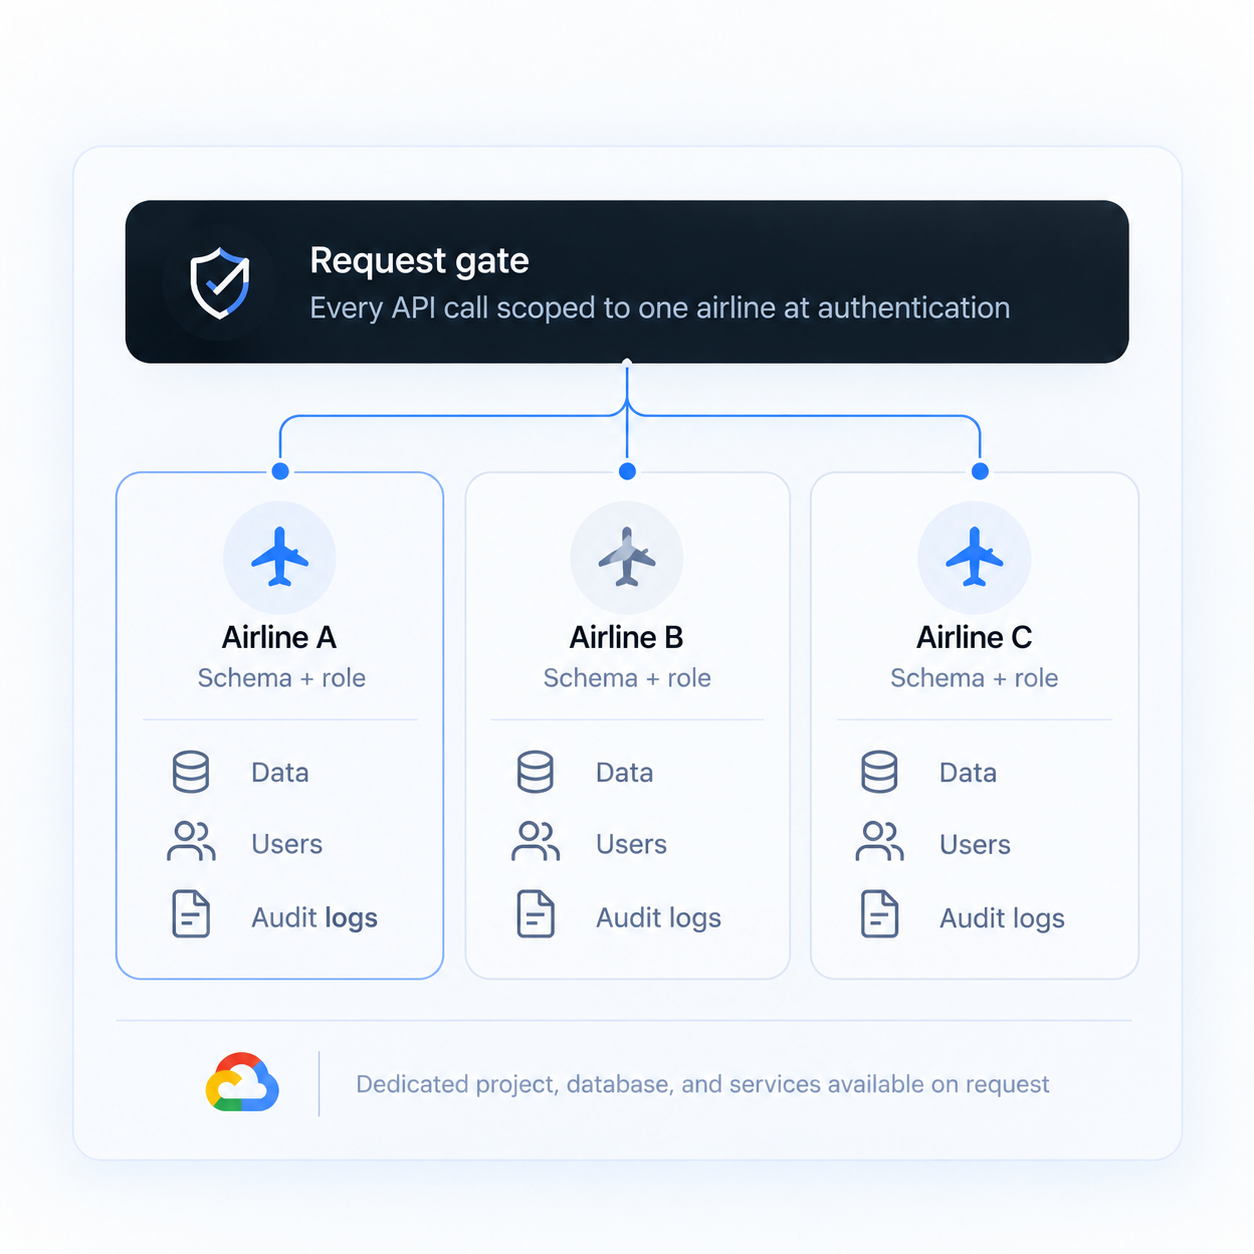
Each airline has its own PostgreSQL schema and database role. Every API request is scoped to the airline at authentication, and users, configuration, and audit logs are partitioned per carrier.
A dedicated Google Cloud project, database, and service set is available for airlines that require full physical separation.
What runs underneath
Controls in production today.
Cloud architecture
Google Cloud europe-west3. Application services on Cloud Run across multiple zones behind a global HTTPS load balancer. Infrastructure-as-code for every service, database, and network rule.
Encryption
AES-256 at rest with Google-managed keys; payment platform keys customer-managed in Cloud KMS. TLS 1.2 or higher on all external traffic and on every service-to-database connection. Card data tokenized; no PAN stored.
Network defense
Cloud Armor WAF and DDoS protection with a threat-prevention profile on production and daily reporting in front of the payment platform. Internal traffic stays inside a private VPC with no public exposure.
Identity & access
SSO and MFA on every human and vendor account. Named accounts only, no shared logins. Least-privilege IAM roles that auto-expire and recertify every six months. Session tokens in HttpOnly cookies, not browser storage. The airline can suspend any user immediately from the admin panel.
Secure development
Mandatory peer review on every merge. Daily Semgrep SAST and dependency vulnerability scanning on every repository. Behavioral malware scanning, install-script lockdown, and dependency pinning on every package install. Strict CSP and security-header baseline on all web apps.
Vulnerability management
Monthly patching. Quarterly external ASV scans and internal vulnerability scans, semi-annual segmentation testing, and annual internal, external, and application penetration tests by an independent third party under the PCI cycle.
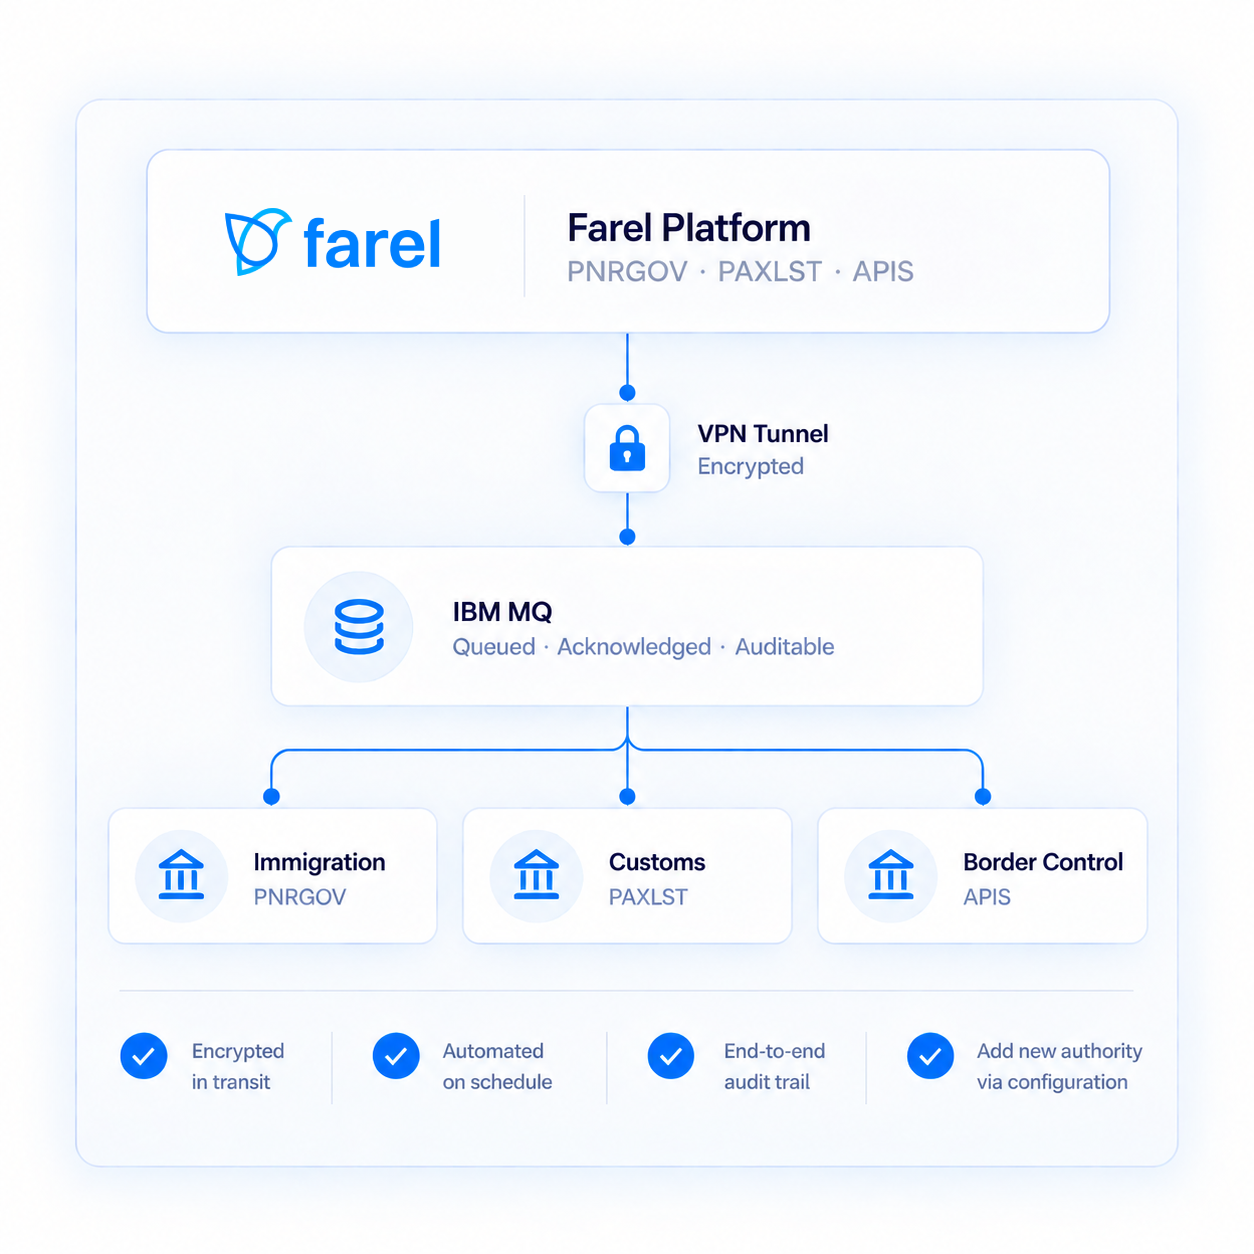

PNRGOV, PAXLST, APIS - over MQ and VPN, not FTP
Regulatory traffic moves through IBM MQ inside VPN tunnels to each authority. Manifests and advance passenger data leave the platform encrypted, on schedule, and auditable end to end.
Adding a new border authority when you open a route is configuration, not a project.

Bots don't get to block your seats
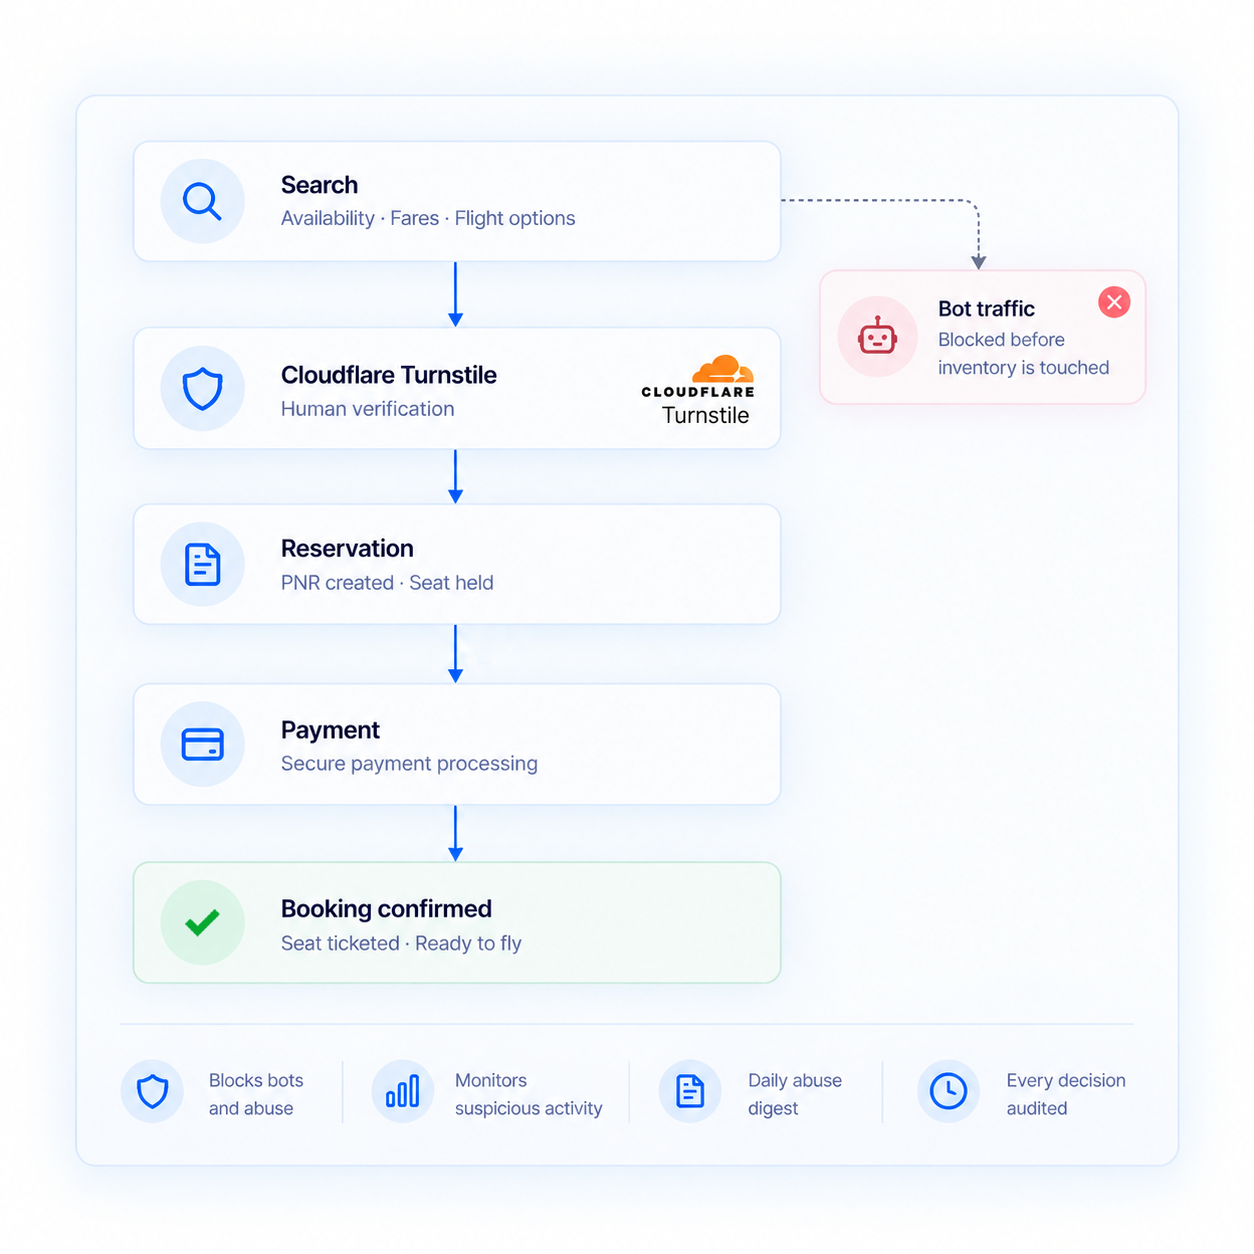
Cloudflare Turnstile gates booking creation and OTP delivery. Every airline runs monitor-first, then enforce, with a daily abuse digest and an audit log of every rate-limit decision.
Stops speculative holds, OTP pumping, and scripted account creation before inventory is touched.
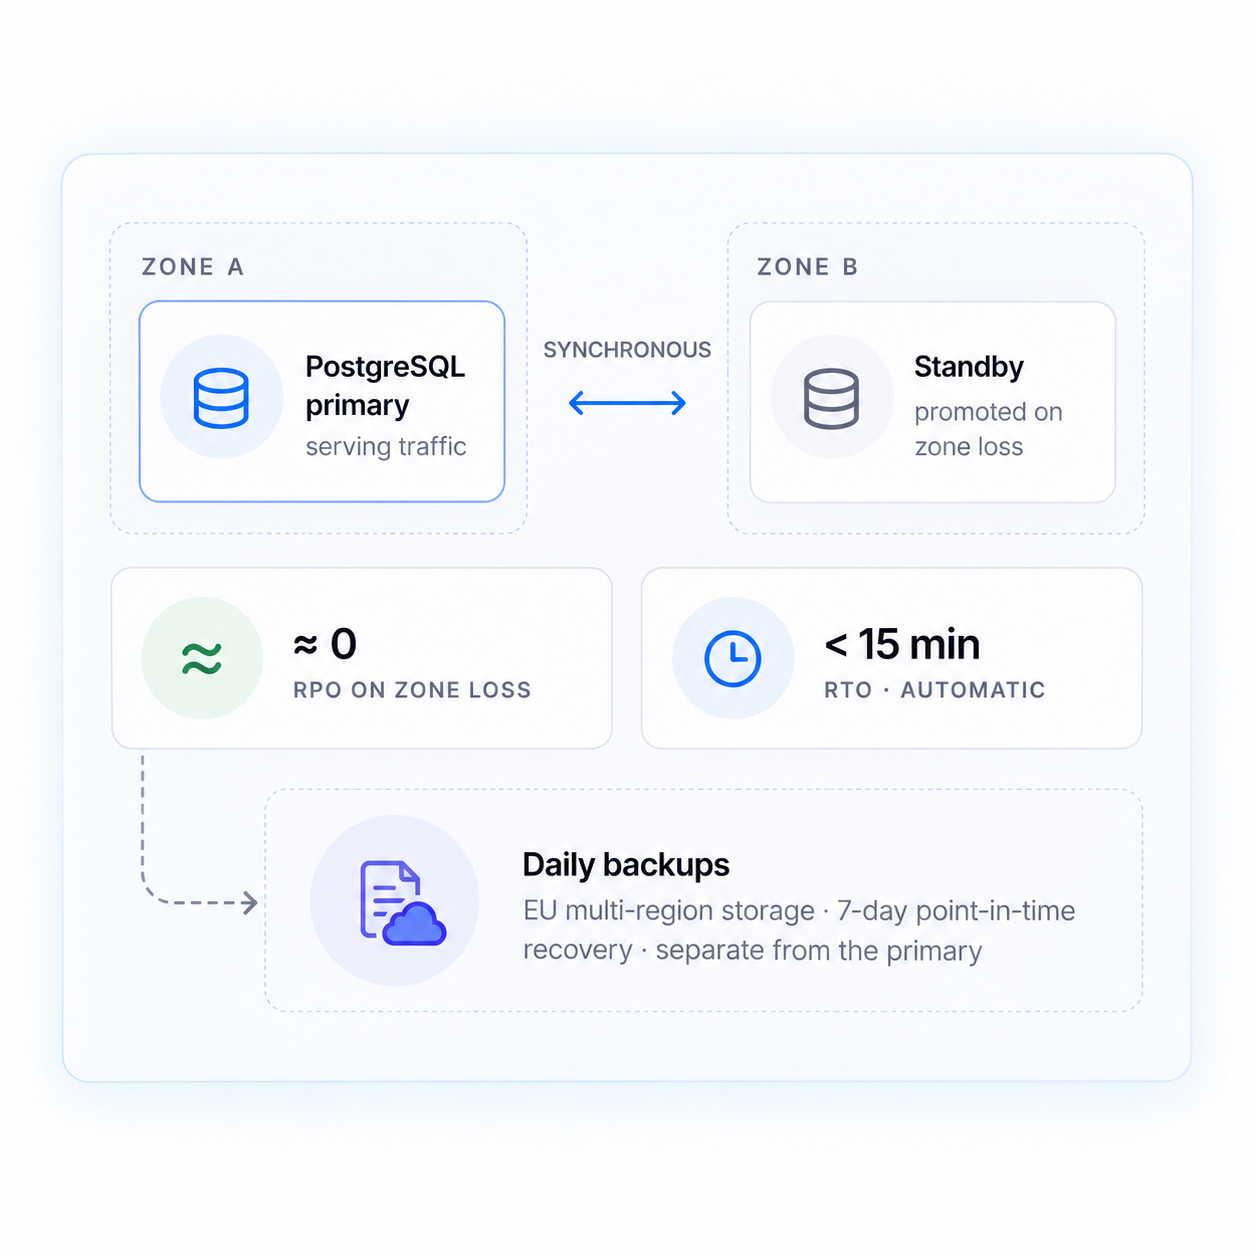

Zone failure recovers in under 15 minutes. Automatically
PostgreSQL runs in regional high availability with a synchronous standby in a second zone - RPO near zero, RTO under 15 minutes on zone loss.
Daily backups with 7-day point-in-time recovery, stored in EU multi-region storage separate from the primary instance. Regional failure: restore into another region, up to 24 hours.
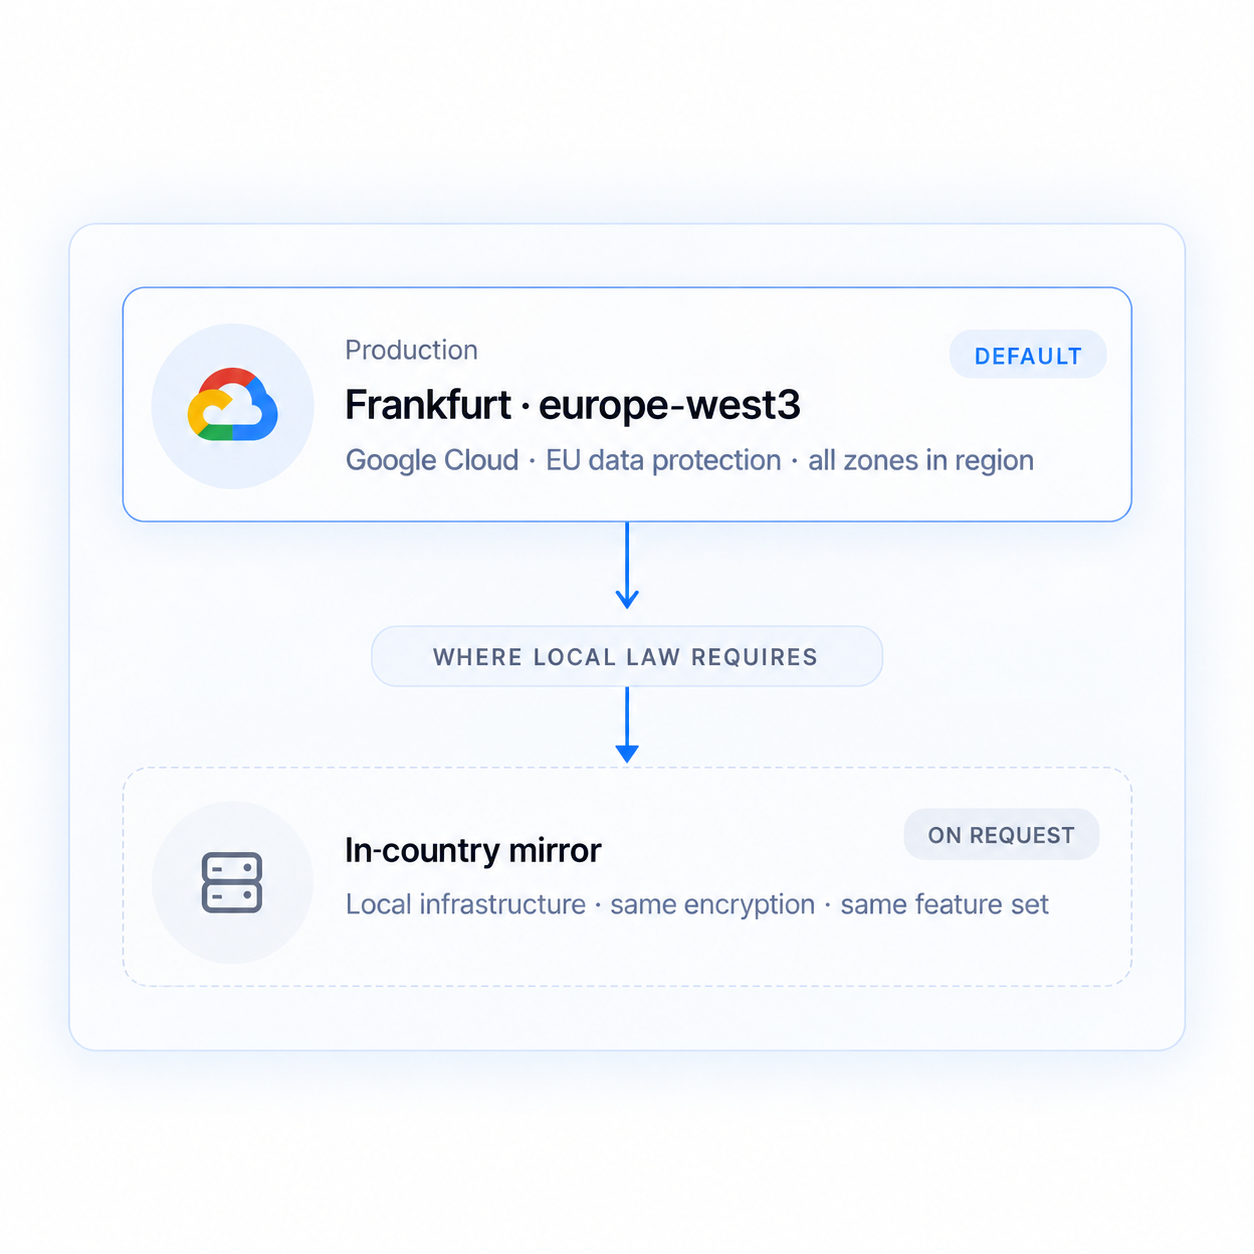

Frankfurt by default. In-country where the law requires it
Production runs in Google Cloud europe-west3, Frankfurt, under EU data protection.
Where local regulation requires in-country residence, we mirror to local infrastructure with no break in encryption or feature parity.
Compliance & assurance
What is held today and what is planned - kept apart on purpose so nothing reads as more than it is.
PCI DSS v4.0.1
Service-provider level, assessed annually by an independent QSA. 2026 assessment completed August 2026; Attestation of Compliance issuing. Scope reduced to SAQ A through processor-hosted card fields.
Independent penetration testing
Internal, external, and application tests, most recent July-August 2026. Executive summaries shareable under NDA.
GDPR and CCPA
Documented retention schedules. Data Processing Addendum available to every customer.
Read the DPAPeople
Annual security awareness and secure-development training for all staff. Background checks on hire.
Full data portability
API, scheduled export, or full database dump at any time. No exit or extraction fees.
Formal backup restoration test
Container image scanning and CI security gate blocking critical findings
Extended alerting on cloud audit events and authentication anomalies
SOC 2 Type II
Timeline shared on request.
ISO 27001
Timeline shared on request.
Trust & transparency
What you can request or read today, and what is still being built.
Penetration test summary
Executive summary of the most recent internal, external, and application tests, shared under NDA.
Request via emailSub-processors list
Every third party that processes customer data on Farel's behalf, with location and purpose.
View the listStatus page
Public uptime and incident history for the platform.
Vulnerability disclosure
Report a security issue by email today. A formal disclosure programme is in preparation.
Report an issueFAQ
Before your security review
Answers to the questions we hear most from airline IT and compliance teams.
Everything your airline needs, in one place
From inventory to check-in, see how each module fits together to streamline your airline operations
Inventory & Pricing
Optimize every seat, maximize every flight
Manage seat availability, fare structures, and revenue logic across all distribution channels.


Security questions before procurement?
Book a working session with our security team on your compliance, residency, and integration requirements.